Advisory details:
github_osv / GHSA-fj52-5g4h-gmq8
| Advisory ID | github_osv/GHSA-fj52-5g4h-gmq8 |
| Aliases | |
| Summary | pyLoad's Session Not Invalidated After Permission Changes ### Summary The `pyload` application does not properly invalidate or modify sessions upon changes made to a user's permissions. ### Details Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the `pyload` application, as a user with a valid session can still perform the actions. ### PoC Take a user with all the permissions, as shown below. 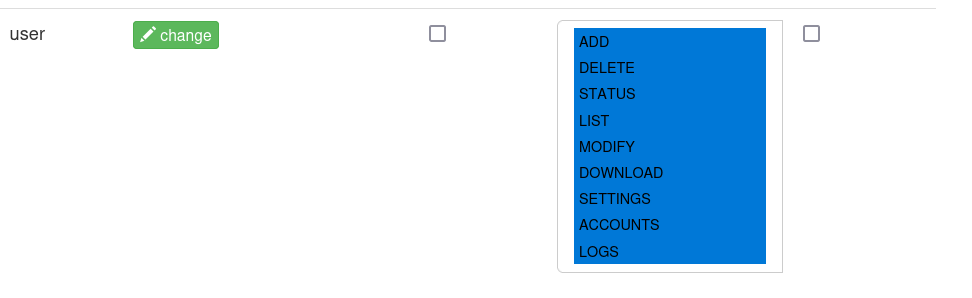 We now log in as this user. 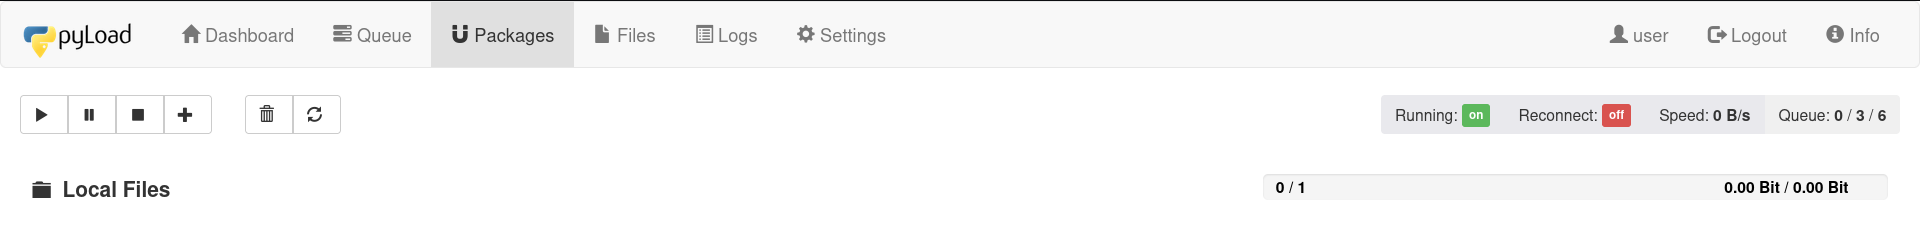 Let us now take away all the permissions. 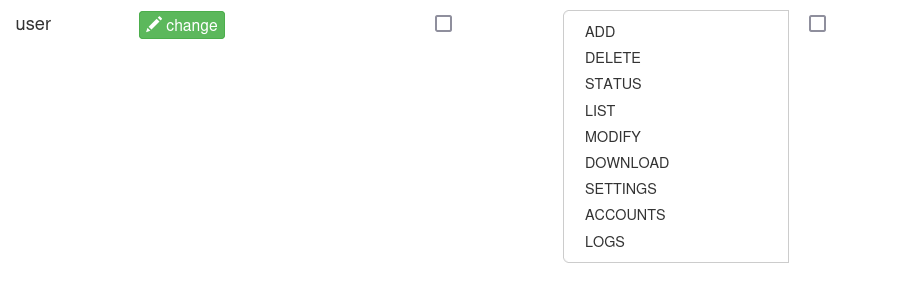 The logged in session can still be used to access everything in the application. 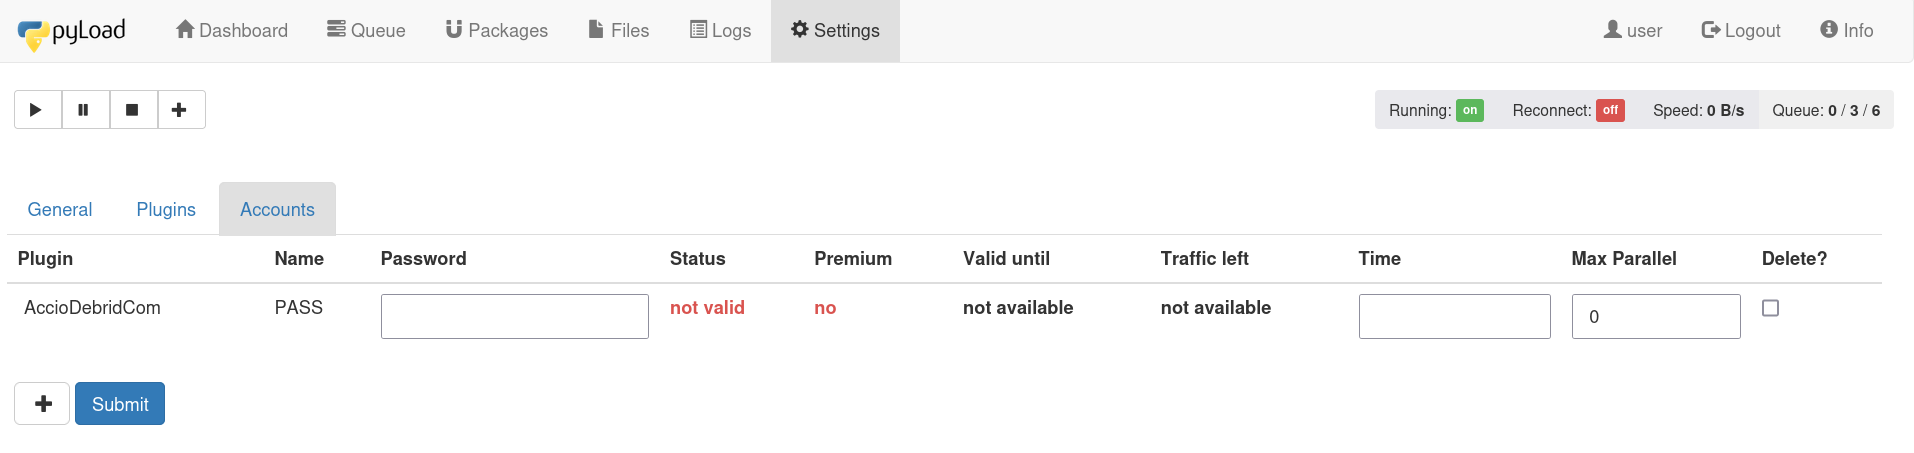 ### Impact Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore. |
| Status | Published |
| Exploitability | 0.5 |
| Weighted Severity | 2.6 |
| Risk | 1.3 |
| Affected and Fixed Packages | Package Details |
| Introduced and Fixed Package Commit Patches | Package Commit Patches Details |
| CWE-613 | Insufficient Session Expiration |
| System | Score | Found at |
|---|---|---|
| cvssv4 | 2.9 | https://github.com/github/advisory-database/blob/main/advisories/github-reviewed/2026/04/GHSA-fj52-5g4h-gmq8/GHSA-fj52-5g4h-gmq8.json |
| generic_textual | LOW |
No EPSS data available for this advisory.
| Patch URL | |
|---|---|
| There are no known patches. | |
| Attack Vector (AV) | Attack Complexity (AC) | Attack Requirements (AT) | Privileges Required (PR) | User Interaction (UI) | Vulnerable System Impact Confidentiality (VC) | Vulnerable System Impact Integrity (VI) | Vulnerable System Impact Availability (VA) | Subsequent System Impact Confidentiality (SC) | Subsequent System Impact Integrity (SI) | Subsequent System Impact Availability (SA) |
|---|---|---|---|---|---|---|---|---|---|---|
network adjacent local physical |
low high |
none present |
none low high |
none passive active |
high low none |
high low none |
high low none |
high low none |
high low none |
high low none |
There are no SSVC decisions available.