Staging Environment: Content and features may be unstable or change without notice.

Advisory Weakness Curation

CVE-2020-26231

Progress 0 / 0

Advisory Summaries

github_osv/GHSA-r89v-cgv7-3jhx

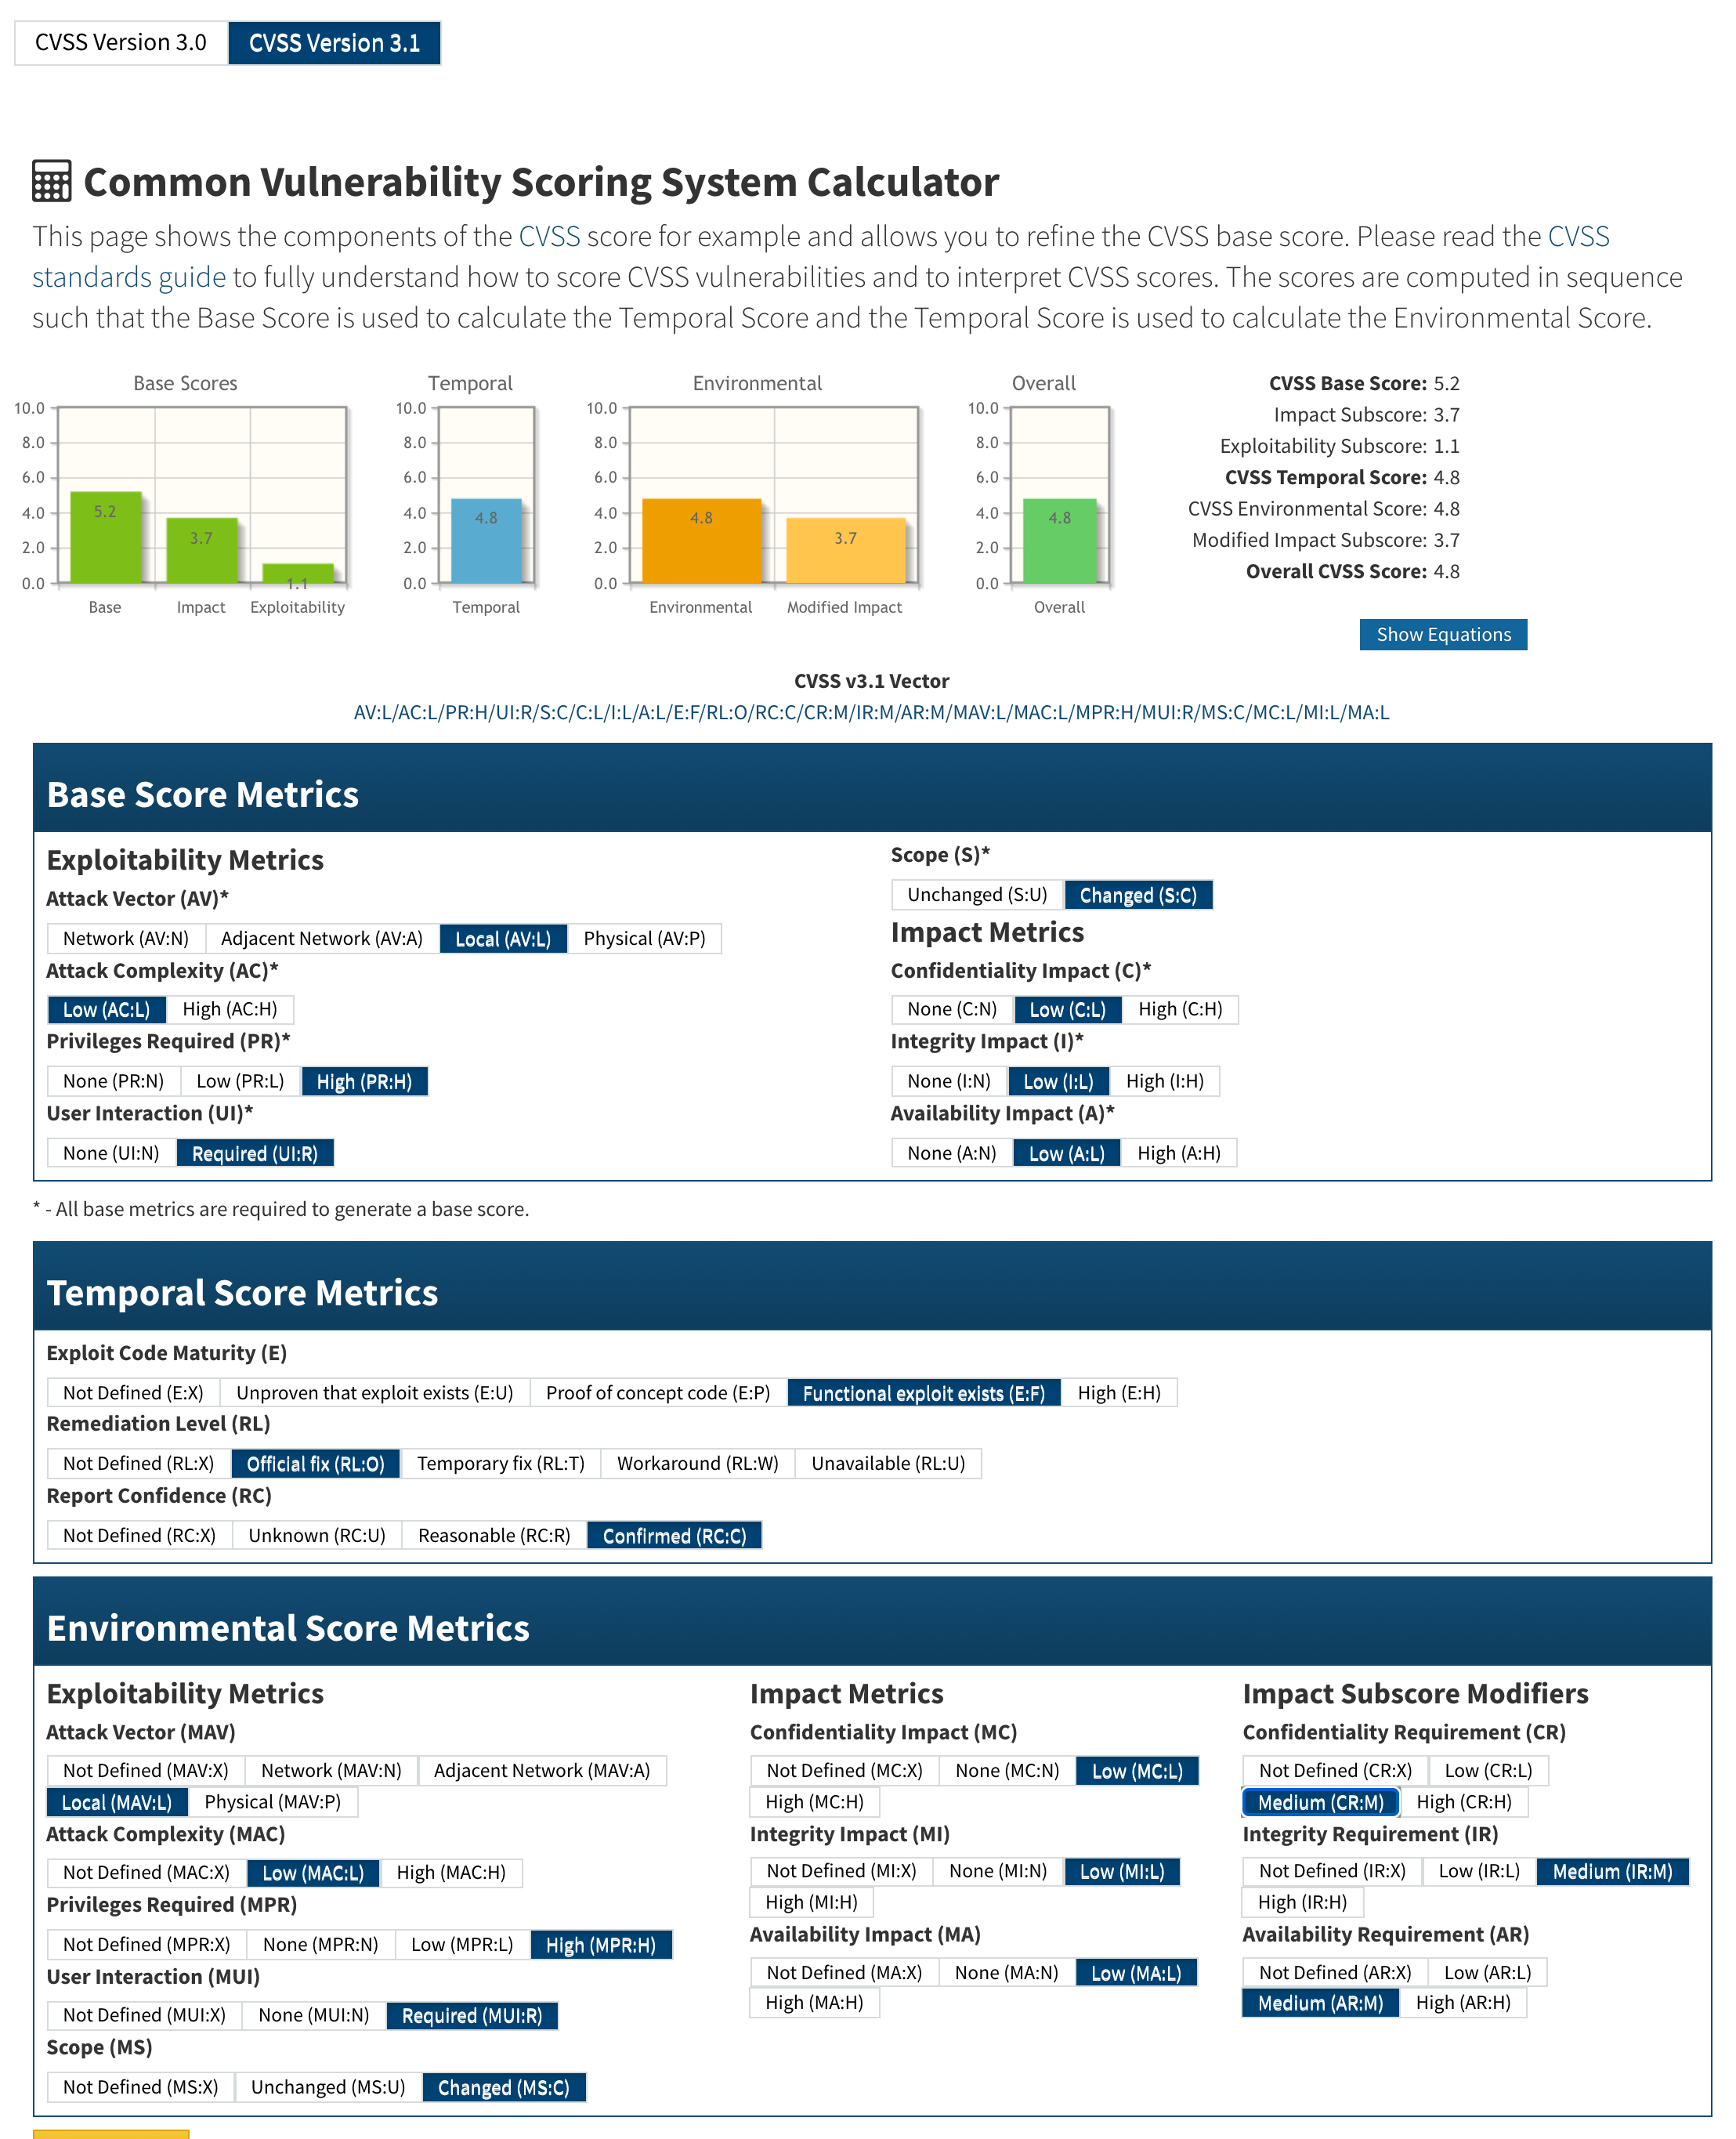
Bypass of fix for CVE-2020-15247, Twig sandbox escape ### Impact A bypass of CVE-2020-15247 (fixed in 1.0.469 and 1.1.0) was discovered that has the same impact as CVE-2020-15247: An authenticated backend user with the `cms.manage_pages`, `cms.manage_layouts`, or `cms.manage_partials` permissions who would **normally** not be permitted to provide PHP code to be executed by the CMS due to `cms.enableSafeMode` being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP. This is not a problem for anyone that trusts their users with those permissions to normally write & manage PHP within the CMS by not having `cms.enableSafeMode` enabled, but would be a problem for anyone relying on `cms.enableSafeMode` to ensure that users with those permissions in production do not have access to write & execute arbitrary PHP. ### Patches Issue has been patched in Build 470 (v1.0.470) and v1.1.1. ### Workarounds Apply https://github.com/octobercms/october/commit/d34fb8ab51108495a9a651b841202d935f4e12f7 to your installation manually if unable to upgrade to Build 470 or v1.1.1. ### References Reported by ka1n4t https://github.com/ka1n4t ### For more information If you have any questions or comments about this advisory: * Email us at [hello@octobercms.com](mailto:hello@octobercms.com) ### Threat assessment: <img width="1108" alt="Screen Shot 2020-10-10 at 1 21 13 PM" src="https://user-images.githubusercontent.com/7253840/95663316-7de28b80-0afb-11eb-999d-a6526cf78709.png">
gitlab/packagist/october/cms/CVE-2020-26231

Missing Authorization October is a free, open-source, self-hosted CMS platform based on the Laravel PHP Framework. A bypass of CVE-2020-15247 (fixed in 1.0.469 and 1.1.0) was discovered that has the same impact as CVE-2020-15247. An authenticated backend user with the cms.manage_pages, cms.manage_layouts, or cms.manage_partials permissions who would normally not be permitted to provide PHP code to be executed by the CMS due to cms.enableSafeMode being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP. This is not a problem for anyone that trusts their users with those permissions to normally write & manage PHP within the CMS by not having cms.enableSafeMode enabled, but would be a problem for anyone relying on cms.enableSafeMode to ensure that users with those permissions in production do not have access to write & execute arbitrary PHP. Issue has been patched in Build 470 (v1.0.470) and v1.1.1.

gitlab/packagist/october/october/CVE-2020-26231

Missing Authorization An authenticated backend user with the `cms.manage_pages`, `cms.manage_layouts`, or `cms.manage_partials` permissions who would normally not be permitted to provide PHP code to be executed by the CMS due to `cms.enableSafeMode` being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP.